ExeWrap: your Windows application as a single EXE, with nothing unpacked
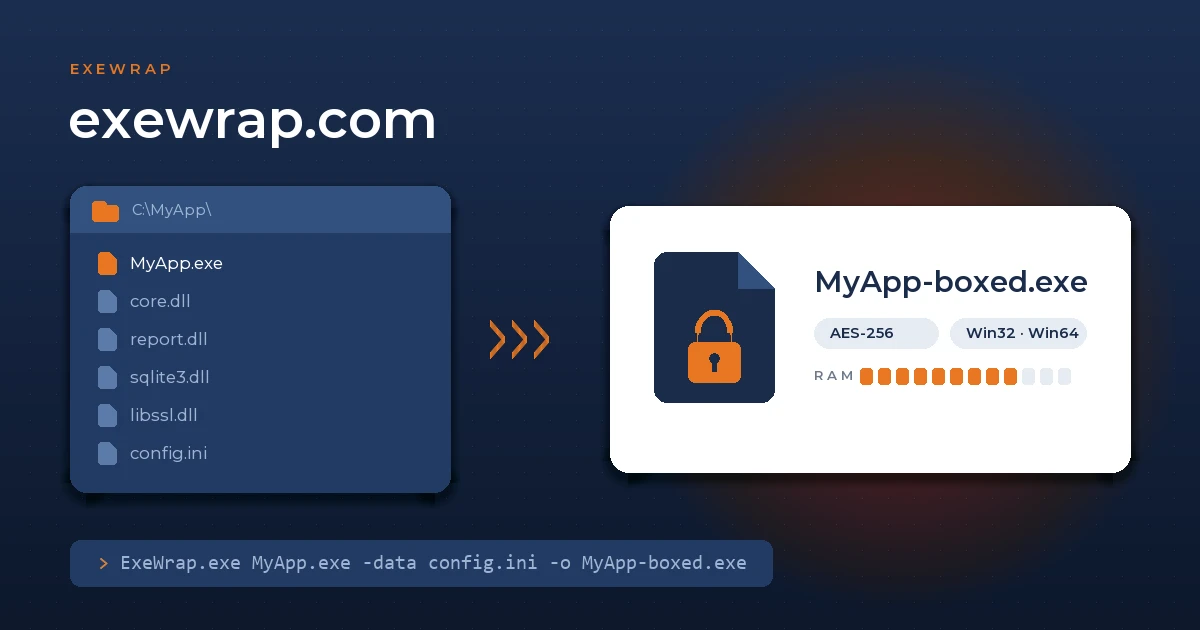
With exewrap.com, Apptimate launches a new product: ExeWrap bundles a Windows application with all its DLLs and data files into one self-contained EXE that runs entirely from memory. Nothing is unpacked to disk, everything is AES-256 encrypted by default, and there is a free demo.
Shipping Windows software rarely means shipping one file. Next to the .exe sit DLLs, configuration files and sometimes registry settings or COM components that have to be registered first. That means an installer, administrator rights and the familiar complaints: a missing DLL, the wrong version, a folder someone tidied up by accident. That is why Apptimate developed ExeWrap, available as of now at exewrap.com.
Virtualisation, not extraction
Other tools can pack an application into a single file, but most of them quietly extract everything to %TEMP% at startup and run it from there. Your DLLs and data then end up loose on disk after all, readable by anyone. ExeWrap does not do that. Its own PE loader maps every bundled module straight into memory; the payload never lands in a temporary folder or the application folder. If you want to check, Process Monitor will show you.
What ExeWrap does
- One file – the main EXE, the DLLs it needs and your data files go into a single output file. Dependencies are detected automatically.
- Virtual file system – your application reads, seeks and enumerates its files as if they were on disk. Writes go to an in-memory overlay or, if you prefer, to an encrypted cache file.
- Virtual registry – registry settings ship as a
.regexport, and in-process COM servers work without anything being registered. - Encrypted by default – every packaged application is AES-256 encrypted, directory included. A password can be added on top.
- Signed updates – small update packages instead of reshipping the whole file every time; replacing a DLL requires an RSA-signed patch.
- Code signing – the result can be Authenticode-signed, so users and systems can verify where it came from.
Which software?
ExeWrap is a PE loader, not a language runtime. It therefore works with native executables from C, C++, Rust, Go and Delphi, among others, for Win32 and Win64, with or without a graphical interface. Framework-dependent .NET Core applications are supported too. Out of scope are drivers and Windows services, the older .NET Framework and out-of-process COM. Like PasGuard, ExeWrap fits into a build pipeline: there is a graphical interface as well as a command-line version.
ExeWrap.exe MyApp.exe -data config.ini -o MyApp-boxed.exe
Trying and buying
The demo is free and stays free; its output carries a watermark. Paid editions come as Standard and Professional, with Enterprise on request. A licence is per developer, works fully offline and never phones home. Applications you have already packaged keep working after your subscription ends. Current prices are on the site.
To be clear: no software protection is a hundred percent secure, and ExeWrap does not claim to be. It does make shipping a great deal simpler and raises the bar considerably for anyone who wants to poke around inside your application. Combine it with PasGuard and the code itself is protected against reverse engineering as well.
Download the demo at exewrap.com. Not sure whether your application will package cleanly? Get in touch – we are happy to take a look with you.
